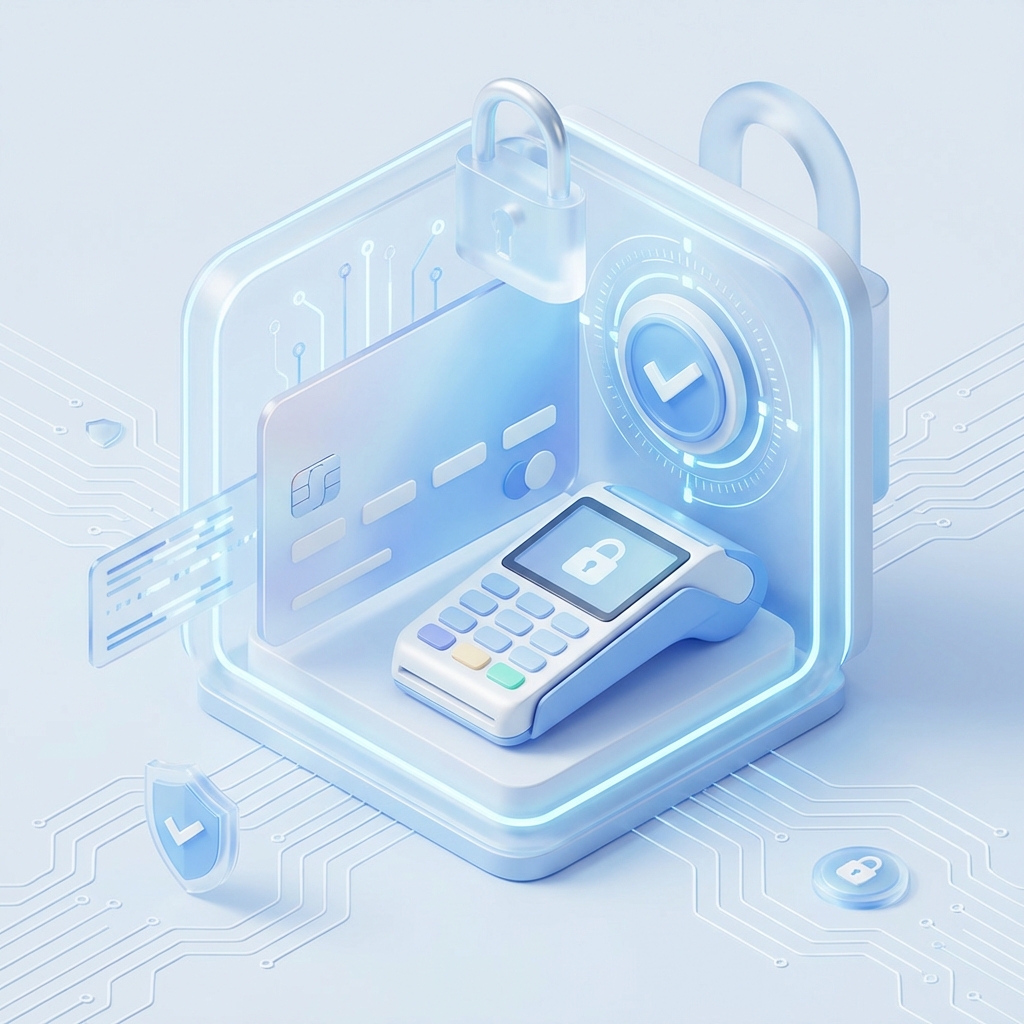
Processing payment cards requires strict adherence to PCI DSS. Failure to comply can result in massive fines. Monitoring access to cardholder data and maintaining secure configurations is a constant demand.
Meet PCI DSS requirements confidently. ManageEngine solutions help you secure networks, encrypt data transmission, manage vulnerabilities, and monitor all access to cardholder data environments in real-time.
Contact Us
Secure cardholder data storage and transmission.
Track and log all access to network resources and card data.
Generate out-of-the-box reports for PCI DSS assessments.
Protect cardholder data environments (CDE) from exposure to untrusted networks. Configure robust firewall rules, apply critical system configurations, and prevent the use of default passwords to dramatically reduce your organization's attack surface.
Discover regulated data within your CDE and implement strict retention policies. Ensure that any stored payment information is masked or hashed, and completely protect data in transit using highly secure end-to-end 256-bit AES encryption.
Scan and remediate high-risk system vulnerabilities with automated, zero-touch patching. Simultaneously enforce Role-Based Access Control (RBAC) and Multi-Factor Authentication (MFA) to restrict system privileges to the absolute minimum necessary.
Audit user activity within the CDE in real time to swiftly identify anomalies. Track administrative file changes, backup audit trails to centralized log servers to prevent tampering, and run periodic wireless network scans to maintain a tightly secured perimeter.
PCI DSS is a global standard published by the PCI Security Standards Council, and it reaches Canadian merchants the same way it reaches US ones: through card-network and acquirer contracts. The wrinkles here are Interac's separate certification, PIPEDA's overlap on cardholder data, and cross-border data flows to US-based processors.
Visa, Mastercard, American Express, and Discover contractually require PCI DSS compliance from every merchant, and their Canadian acquirers - Moneris, Chase Merchant Services Canada, Global Payments, Elavon Canada, Fiserv, and TD Merchant Solutions - pass those requirements down through merchant agreements. There is no separate "Canadian PCI DSS." The same standard applies, enforced by the same card brands.
Interac Debit runs on a separate network with its own PIN pad approval and terminal certification requirements, distinct from card-scheme PCI. Merchants accepting both credit and Interac end up managing two overlapping compliance programs on the same POS estate. Endpoint patching, terminal firmware tracking, and configuration baselining apply to both regardless of which standard drove them.
Cardholder data is personal information under Canada's PIPEDA, so a PCI DSS breach is usually also a privacy breach with breach-notification obligations to the Office of the Privacy Commissioner and to affected individuals. Retention limits and access-audit trails serve both regimes simultaneously - one set of controls, two audiences.
Most Canadian merchants route payments through processors with US-based infrastructure. Cardholder data crosses the border every transaction. PIPEDA does not prohibit this, but it does require disclosure to customers that personal information may be processed abroad, plus contractual safeguards with the processor. Consult our retail solutions page for how this shows up in day-to-day POS environments.
Yes. PCI DSS is a global card-network standard, not a US-only one. If your business accepts Visa, Mastercard, American Express, or Discover in Canada, your acquirer's merchant agreement obligates you to comply. Your validation level (Level 1 through 4) depends on annual card-transaction volume, not geography.
No. Interac runs its own certification and approval program for debit terminals and PIN pads, separate from PCI DSS. If you process both credit and Interac, you manage two overlapping programs. The good news: the underlying IT controls (patching, access audit, configuration baselining) satisfy both when done once at the endpoint layer.
Almost always. Cardholder data qualifies as personal information under PIPEDA, which means a breach triggers Canadian privacy-law obligations on top of the card-brand fine schedule. Log360, ADAudit Plus, and DataSecurity Plus produce the audit trails and access logs that both regimes ask for.
The Payment Card Industry Data Security Standard is a set of security requirements maintained by the PCI Security Standards Council. It covers how merchants and processors store, transmit, and protect cardholder data across 12 requirement areas, from network segmentation to access control to logging.
PCI DSS v4.0's 12 requirements are broad and hard to satisfy natively. ManageEngine's suite covers vulnerability scanning, patch automation, MFA, encryption enforcement, tamper-resistant audit trails, and least-privilege access from one vendor, which simplifies both the compliance work and the reporting a QSA sees.

Unified SIEM with pre-built PCI DSS report templates covering log collection, retention, and correlation across the CDE.

Real-time Active Directory auditing for access-control tracking, privileged-account monitoring, and audit-trail integrity.

Cardholder data discovery, file-access auditing, and DLP enforcement for the storage side of the CDE.

Continuous vulnerability scanning, prioritization, and automated patching to meet the "maintain a vulnerability management program" requirement.

Privileged access management and password vaulting for shared administrative accounts on POS servers and CDE infrastructure.
Unified endpoint management for POS terminals, kiosks, and staff workstations with patch, configuration, and hardening controls.